About · CV

Rafał Charciarek

Application security tester WordPress websites

I test the security of web applications using the OWASP Top 10 methodology, and I also build WordPress websites and Flutter apps. I do websites and security together because I know how websites break: finding that is my job.

I have a job, but I can take on additional commissions.

Write about a commissionDownload CV (PDF)One A4 page, same content as here. PL (PDF)
  • Exact Forestall S.A.application security tester
  • OWASP Top 10testing methodology
  • ISO 27001Lead Auditor
  • 10courses and certificates
  • C1English

01 Experience

Work experience

  1. 2026 – present now

    Application Security Tester

    Exact Forestall S.A.

    Manual penetration testing of web applications following the OWASP Top 10 methodology.

  2. 2025 – 2026

    Application Tester

    Exact Forestall S.A.

    Designing and running test scenarios for system modules and reporting defects in the development environment.

  3. 2024 – 2025

    Sales Specialist

    Exact Forestall S.A.

    Winning foreign business clients and advising on the company’s solutions.

EarlierMilitary service in the 131st BLP (2020–2024). Sales and customer service: Fonmix (2019–2020), Wójcik Motors (2018–2019). Production and assembly: X-Kom (2017–2018), English Braids (2016), Bosch Termotechnik (2014–2016), CGR Polska (2011–2013).

02 Main project

Rysa: a network audit app

Rysa

An Android app I wrote to audit my own network. It runs nmap in Kali NetHunter on a rooted phone and turns the results into a prioritised report.

I scanned Metasploitable 2 with it, a deliberately vulnerable lab machine. The result is a 79-page report. It is an exercise in my own lab, with no client.

See how Rysa works

Sample report from Rysa · A scan of a Metasploitable 2 machine

  • criticalvsftpd 2.3.4 with a backdoor (CVE-2011-2523, CVSS 10.0) and anonymous access.
  • criticalAn open administrator shell on port 1524 with no authentication.
  • criticalMySQL 5.0.51a with an empty root password; the whole file system exported over NFS.
  • 30findings
  • 5critical
  • 7high
  • 2CVEs in the CISA KEV catalog
  • 23public exploits
  1. Scannmap in Kali NetHunter, fixed profiles only.
  2. Read-only layerswhatweb, sslyze, ssh-audit, dig, p0f, UPnP. No logins, no exploits.
  3. CorrelationNVD, OSV.dev and CISA KEV. Exploit-DB as metadata only.
  4. AI write-upGemini explains each finding after pseudonymisation; a validator rejects made-up CVEs.
  5. ReportPDF: remediation plan, evidence and a confidence level for every result.
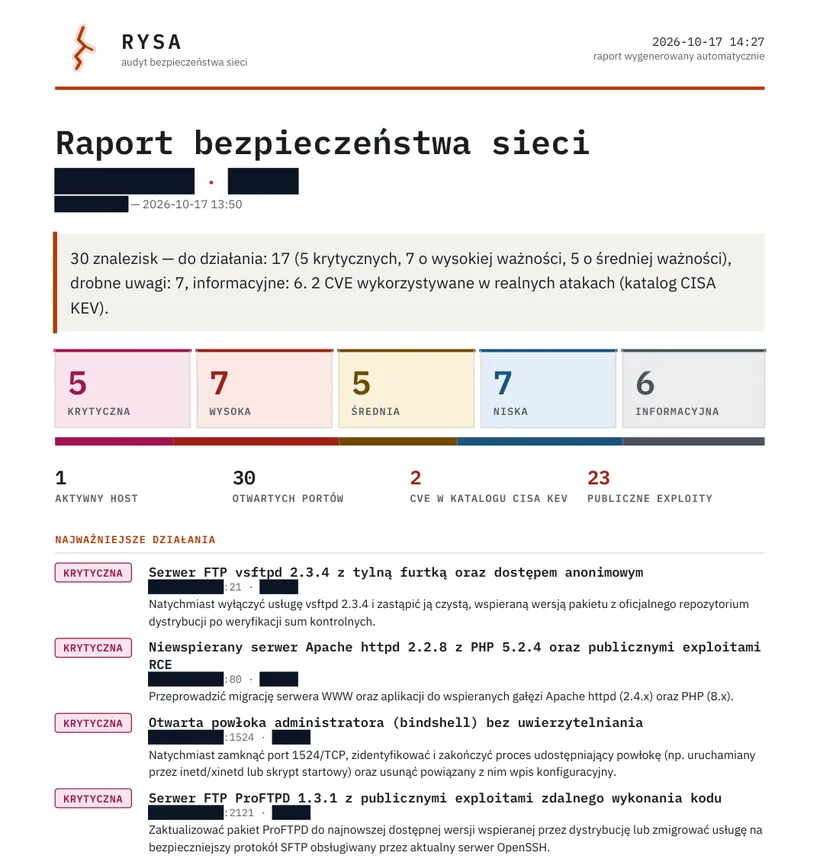
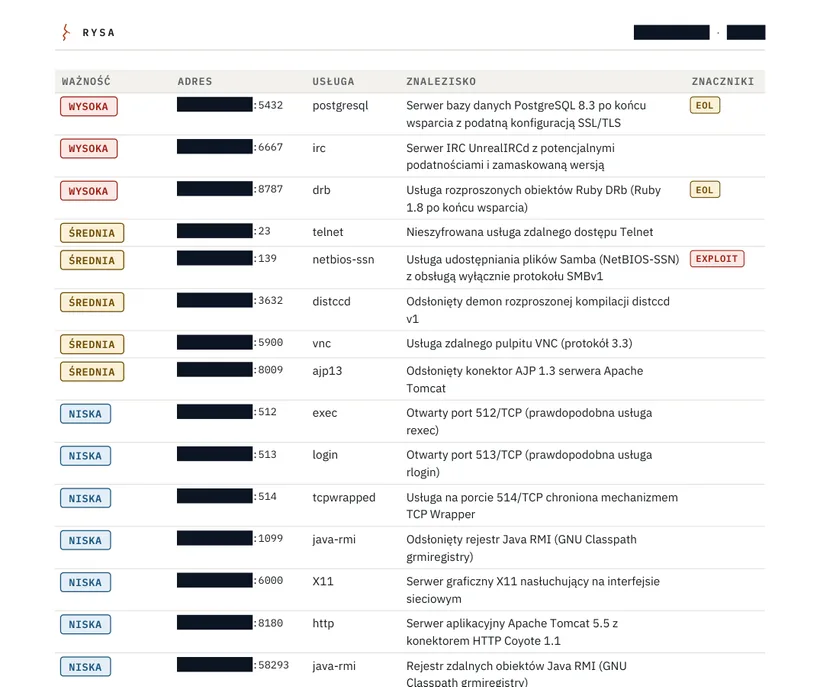
First page of the Rysa report: summary of 30 findings, the critical count and the most important actions.Part of the findings matrix from the Rysa report: severity, service, description and tags.
Report screenshots (network data masked)

The report has a remediation plan (now, soon, while you are there), scan evidence and verification steps. Rysa itself points out that a human has to confirm the findings.

A Flutter (Dart) app, a Python (FastAPI) backend, over a thousand automated tests.

How Rysa works: technical details
  1. Scan. nmap in Kali NetHunter (a chroot on a rooted phone), commands built only from fixed profiles: no free-form flags, NSE scripts only from safe categories, and a target outside the allowed list needs a confirmation that I have the right to scan it.
  2. Read-only layers. whatweb (site technologies), sslyze (TLS), ssh-audit, dig (DNS resolver), p0f (passive OS fingerprinting), UPnP read from the router and the phone’s Wi-Fi security. No login attempts and no exploiting.
  3. Correlation with databases. Detected versions are matched against NVD, OSV.dev and the CISA KEV catalog (CVSS, vulnerabilities exploited in attacks). Exploit-DB is used only as metadata: I check whether an entry exists and never download its content.
  4. A description from an AI model. A Gemini model writes in Polish why a finding has its severity and how to check it without intrusion. Before that, IP addresses, MAC suffixes and host names are replaced with placeholders, and a separate validator rejects invented CVE numbers.
  5. Report. A PDF with a summary, a remediation plan, evidence and a list of gaps in the reconnaissance. Every result has a source and a confidence level, so a confirmed vulnerability is not mistaken for a match by version number.

nmap (Kali NetHunter) → whatweb, sslyze, ssh-audit, dig, p0f, UPnP → NVD, OSV.dev, CISA KEV, Exploit-DB (metadata) → a Gemini model with pseudonymisation and a CVE validator → PDF report.

03 Skills

Skills

Apps and web 11

WordPress Next.js React Astro Flutter / Dart Kotlin Node.js PostgreSQL Python MS SQL Git

MS SQL: from client audits and migrations, not something I build on from scratch.

Security 10

Burp Suite OWASP ZAP Nmap Wireshark Wazuh SIEM OWASP Top 10 Web attacks (SQLi, XSS) Vulnerability analysis OSINT ISO 27001

Systems and networks 06

Linux (CLI) Bash Windows TCP/IP DNS Firewalls

Tools and automation 05

n8n (workflows) Local LLM models VS Code Android Studio M365

04 Certificates

Certificates and courses

MASTERMIND

ISO/IEC 27001:2022 Lead Auditor

  • EY (Program CRC)Web application penetration testing
  • ING Hubs (Program CRC)Cybersecurity – defense in modern organisations
  • CiscoEthical Hacker, Linux Essentials, Introduction to Cybersecurity
  • SecuritumWAZUH Expert
  • NiebezpiecznikCybersecurity for businesses
  • Akademia WywiaduCybersecurity fundamentals, OSINT
  • NAVOICAFundamentals of network infrastructure
  • Wrocław University of Science and TechnologyAIDEAS (Idea Generator)
  • Rescue House (ITP)First aid instructor course (2026)

05 Own practice

Projects and the lab

Projects from this site

Lab and learning

  • Brownian Motion SimulatorFlutter app.
  • Mobile pentesting platformKali NetHunter on a OnePlus 6T with an AI assistant.
  • Firewall testing scriptsUDP flood and DoS for firewall testing, in my lab.
  • Automation and local modelsLocal LLM models and n8n workflows.
  • Capture the FlagArctic Howl (OffSec): 272nd place of 1546 participants.

06 Education

Education and languages

Education

  • 2024 – present
    Computer ScienceWSB Merito University in Chorzów
  • 2005 – 2009
    High school diploma, ITTechnical Science Schools in Częstochowa

Languages and other

  • Polish (native)
  • English (C1)
  • Driving licence, category B
  • Qualified first aid, rescuer (WCKMed in Łódź)
  • PC and mobile hardware servicing

Ready to start?

Let’s start with a conversation

Describe what you want to build. The reply contains the scope, the price and the timeline. The inquiry costs nothing and commits you to nothing.